Lampost Hash
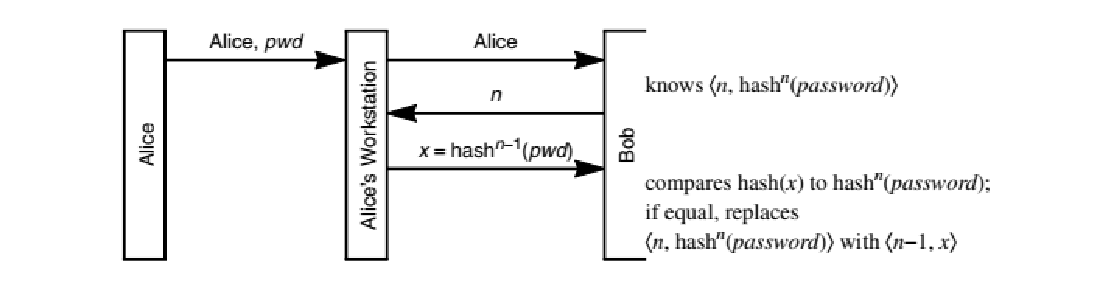
- One time password scheme
- Server B authenticates A
Enhanced Version
- Uses Salting
Advantages
- Two different accounts will have different hashes of the password
- Retain the same password when n=1, just change the salt
- Works against dictionary attacks
Disadvantages
- n logins only
- No mutual authentication
- No shared secret for rest of the conversation
Small n Attack
The hacker can impersonate the server with n’ < n, effectively enabling to login from n’ → n. Counter → Sanity check
Human and Paper Environment
- Code sheet with list of hashes, manual checking